




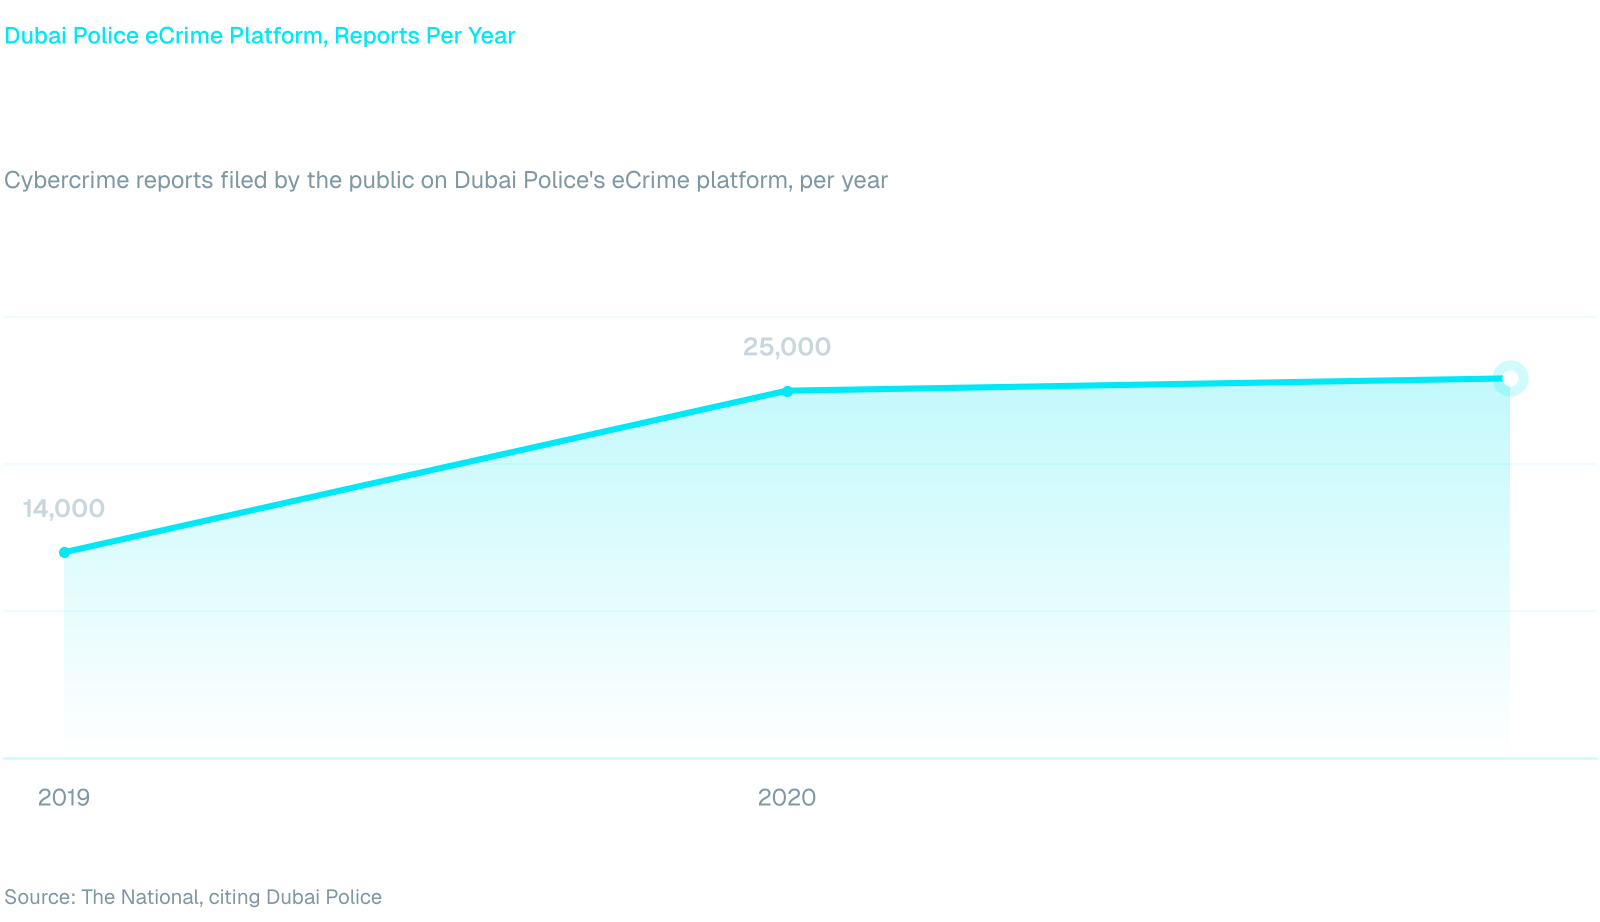
Dubai Police's eCrime platform received 25,841 cybercrime reports from the public in 2021. Residents file those reports after meeting scams, and your employees meet the same kinds of lures at their desks. This post is for the CISO or awareness manager choosing a phishing simulation platform UAE staff will actually learn from.
In short: A phishing simulation platform for the UAE should pick each person's next simulation itself, run in Arabic and English, keep data on UAE or GCC servers or on-premise, and turn every click and every report into a risk score and a response.
What a Phishing Simulation Platform UAE Teams Need
Volume explains why the platform has to keep pace. Reports to the eCrime platform grew from 14,000 in 2019 to a record 25,000 in 2020 and 25,841 in 2021. A yearly round of identical emails cannot match a threat that arrives this often and in this many forms.
A platform that does keep pace does four jobs. It chooses and sends simulations, it writes lures in the languages and contexts your staff work in, it keeps data where your policies say it must stay, and it turns each result into a response for that person. The sections below take those jobs in turn, starting with how simulations run.
Three Ways to Run Simulations
Fraus runs simulations in three modes, so a team can start with the effort it actually has.
Graybait. Graybait is a campaign-less program. Setup is four steps: connect the workforce, set guardrails, choose an objective and activate. It then runs for twelve months, and your team steps in only when the system asks. Agentic AI picks or generates each employee's next simulation from their Human Risk Profile and sets its difficulty, theme, psychological trigger and timing.
Lures match the person's role, context and history. Difficulty rises as someone keeps spotting attacks, and a method is retired once that person has beaten it. Frequency follows each person's risk within the limits the admin sets. For a small team with no time to plan campaigns, this is the mode that fits. The post on autonomous phishing simulation without campaigns goes deeper.
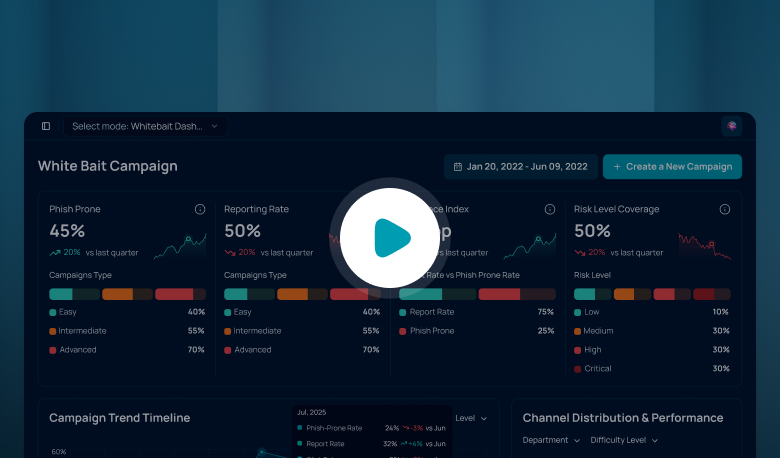
Whitebait. Whitebait is the AI-guided option for teams that want to plan campaigns. It recommends campaigns, covers MFA bypass, QR code and credential harvesting scenarios, and tracks reporting rate next to click rate.
Blackbait. Blackbait runs OSINT reconnaissance on the targets you select and escalates attacks autonomously. It suits the people you choose for deeper testing.
Arabic, Local Lures and Hosting
Staff in the UAE read in Arabic and English, sometimes within the same hour. Fraus is available in both languages and Whitebait carries templates in both, so an Arabic phishing simulation sits in the same platform and the same reports as the English one.
Dolus AI Studio turns an email screenshot or a prompt into an editable simulation template, so a lure your staff received last week can become next week's simulation.
Hosting is the other question a UAE security review raises early. Fraus can be hosted on UAE or GCC servers or deployed fully on-premise. It holds ISO/IEC 27001 certification and UAE Information Assurance (UAE IA) compliance, and is aligned with the NIST Cybersecurity Framework.
What Happens After the Click
A simulation is only worth running if the result changes something for that person. In Odin, results feed a continuous risk score for each employee, weighted by role criticality, with an individual threat profile and automatic escalation.
Zero-Touch Training responds when a person shows a risk. Training matched to the behavior arrives at once, inside Microsoft Teams, with no manual step. The Fraus Teams App adds one-tap phish reporting, so every report is counted next to every click.
Codex supplies the short lessons, which Fraus's agentic AI recommends or assigns from each person's training gaps, in Arabic and English. Agentic automation rules handle follow-up such as notifying a manager, while higher-stakes actions like step-up MFA always wait for analyst approval.
Start With One Group
The 25,841 reports from the opening are the public's side of the same problem your staff face at work. When you compare platforms, the buying questions from hosting to reporting are set out in Phishing Simulation UAE: What to Check Before You Buy.
A practical first step is to pick one department, set the guardrails and activate Graybait for it. After the first month, read reporting rate beside click rate for that group and decide where to extend.
Frequently Asked Questions
What is a phishing simulation platform?
A phishing simulation platform sends realistic fake attacks to employees, records who clicks, who reports and who ignores them, and connects those results to training and risk scoring. The useful ones choose simulations per person, so one employee's lessons do not depend on a company-wide campaign calendar.
Does a platform need Arabic phishing simulation?
If your workforce reads Arabic, yes. A platform that sends only English lures tests only part of your people. Fraus is available in Arabic and English, and Whitebait carries templates in both languages, so results from both groups land in the same reporting.
Can a phishing simulation platform be hosted in the UAE?
Yes. Fraus can be hosted on UAE or GCC servers or deployed fully on-premise. It holds ISO/IEC 27001 certification and UAE IA compliance, and is aligned with the NIST Cybersecurity Framework, which gives your security review the facts it needs on hosting and controls.
How much admin does automated phishing simulation need?
With Graybait, setup is four steps: connect the workforce, set guardrails, choose an objective and activate. It then runs for twelve months with no campaigns to plan, launch or review, and your team steps in only when the system asks for a decision.