Agentic Automation Rules

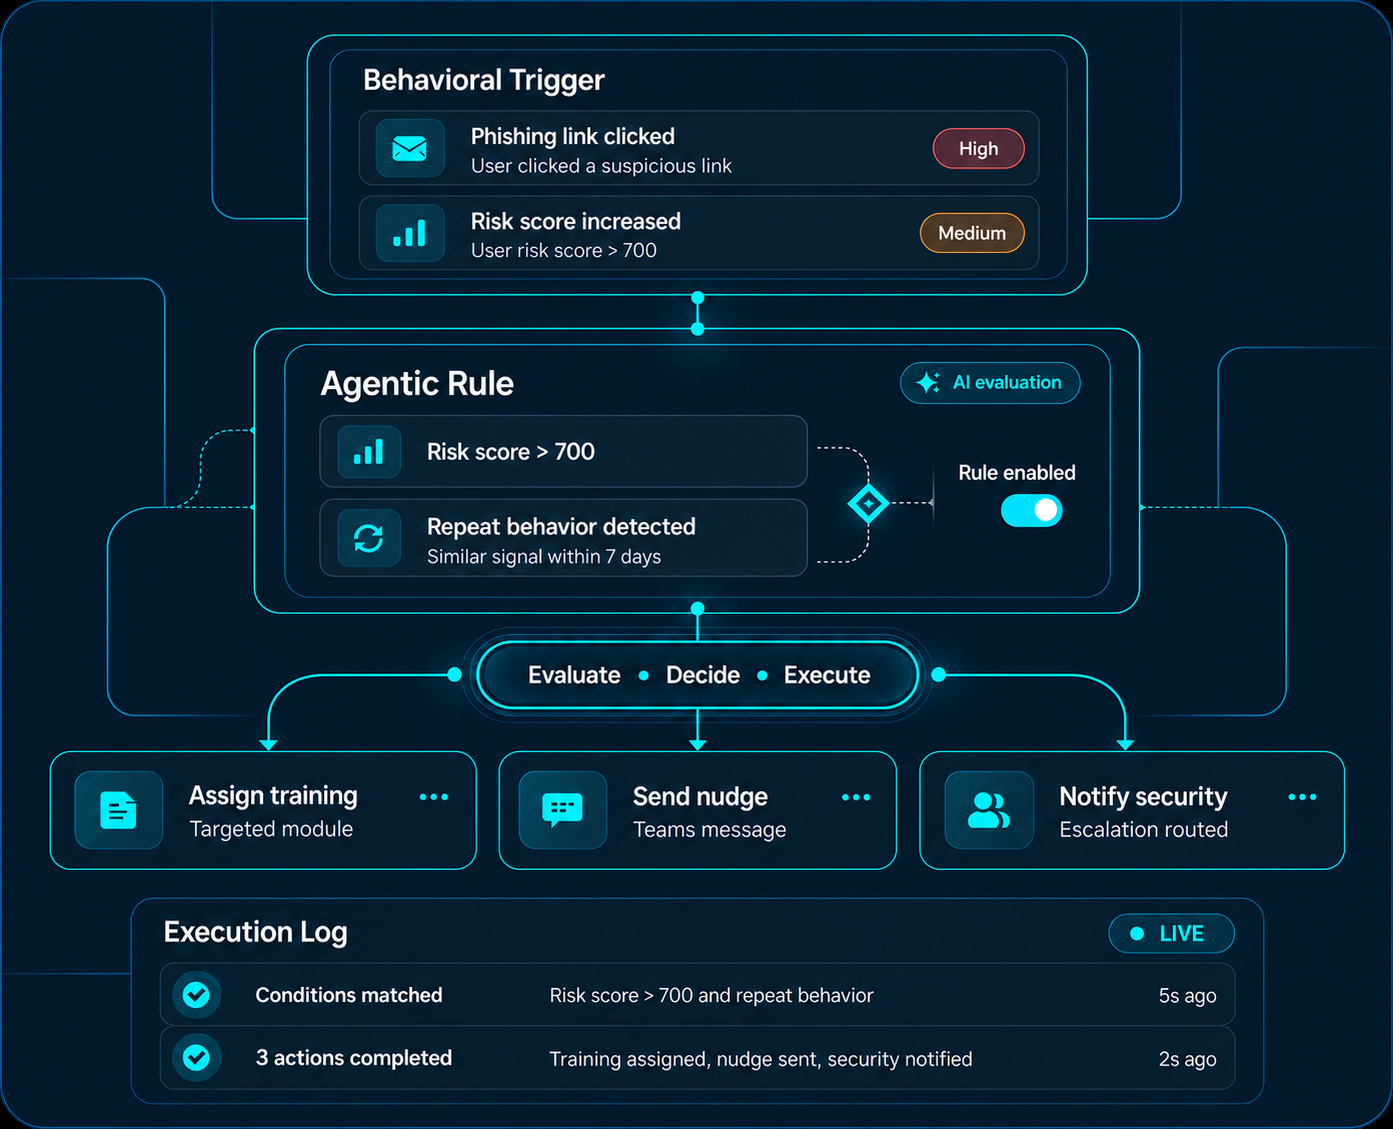
Agentic AI that responds to human risk the moment it appears. Odin watches events across Fraus modules and your security stack, runs the rules you trust, recommends new ones before an incident happens, and steps in on its own when an event falls outside every rule.

‍

Each agentic decision becomes a visible rule, labeled by origin and logged for audit. You decide how much autonomy Odin has: off, supervised with approval by email, or unsupervised after a 30-day trial period. Your team stops building and chasing responses by hand and keeps control of the decisions that matter.

Agentic Automation Rules

Why Rule-Only Automation Falls Behind

Static automation responds only to what someone thought to write a rule for. Everything else waits for a person.

Rules Cover Only What You Predicted

Rules Cover Only What You Predicted

New attack patterns and event types arrive faster than teams can write rules for them, so the newest risks are often the least covered.

Gaps Nobody Is Watching

Gaps Nobody Is Watching

Risky patterns that no rule covers, such as a new inbox rule forwarding mail outside the company, go unnoticed until they become an incident.

Every Response Waits for a Person

Every Response Waits for a Person

Assigning training, alerting managers, and chasing overdue attestations by hand adds administrative work that grows with the workforce and delays every response.

Fixed Responses, No Judgment

Fixed Responses, No Judgment

Responses that ignore role, repeat behavior, and risk level overreact to small slips and underreact to real danger.

Autonomy Without Oversight

Autonomy Without Oversight

AI that acts with no approval path, trial period, or audit trail is hard to trust with higher-stakes actions.

Decisions Nobody Can Explain

Decisions Nobody Can Explain

When no one knows whether a person or a system created a rule, or why, rule sets overlap, drift, and lose credibility.

How Fraus Solves This

Agentic AI that decides and acts on human risk events within the boundaries you set, and turns every decision into a rule your team can see.

01

Agentic Gap Coverage

When an event arrives that no rule covers, Odin evaluates it, writes a contextual rule, and runs the intervention. Rules created by admins or applied from recommendations always take priority, so Odin acts only on genuine gaps.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Three Levels of Autonomy

Off logs uncovered events and takes no action. Supervised sends each proposed intervention to every approver on your list to approve or reject by email. Unsupervised acts immediately once its 30-day trial period, during which it still asks first, is complete. You can change the mode or switch it off at any time.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Test Before You Trust

Simulate a risky event and see, step by step, what Odin would do with your current settings: match an existing rule, log the event, request approval, or act on its own.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Proactive Rule Recommendations

Odin analyzes past history, activity data, business context, and industry standards to find patterns no rule covers, then proposes ready-to-apply rules with estimated 30-day matches and the reasoning behind each one.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Precise Triggers and Audiences

Triggers span seven categories, from Whitebait and Blackbait simulation results to identity, endpoint, data loss prevention, directory, training, and risk score events. Filters, occurrence thresholds, and per-person limits shape when a rule fires, and audiences combine presets, departments, groups synced from Microsoft Entra ID, and named individuals.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Stacked Actions With Approval Gates

One rule can assign nudges, modules, videos, policies, or posters, and notify role groups or the triggering employee's manager by email, Microsoft Teams, or both. Higher-stakes actions, such as step-up MFA on next sign-in or a finance approval hold with callback verification, wait for analyst approval every time. Rules can chain, escalating when another rule's action goes unacknowledged.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Zero-Touch Recurring Work

Scheduled rules run weekly, monthly, quarterly, or annually: executive risk reports, policy re-attestation reminders, refresher training reassignments, risk score recalculation, and simulation campaigns, including Blackbait's AI-generated adaptive-difficulty campaigns.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

01

Every Decision Labeled and Logged

Every rule shows whether it is Admin-defined, an AI Recommendation, Agentic AI · Supervised, or Agentic AI · Unsupervised. Every agentic action is logged for audit, and the rule builder shows a plain-language summary, a technical definition, and a warning when a similar rule already exists.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Agentic Gap Coverage

When an event arrives that no rule covers, Odin evaluates it, writes a contextual rule, and runs the intervention. Rules created by admins or applied from recommendations always take priority, so Odin acts only on genuine gaps.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Three Levels of Autonomy

Off logs uncovered events and takes no action. Supervised sends each proposed intervention to every approver on your list to approve or reject by email. Unsupervised acts immediately once its 30-day trial period, during which it still asks first, is complete. You can change the mode or switch it off at any time.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Test Before You Trust

Simulate a risky event and see, step by step, what Odin would do with your current settings: match an existing rule, log the event, request approval, or act on its own.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Proactive Rule Recommendations

Odin analyzes past history, activity data, business context, and industry standards to find patterns no rule covers, then proposes ready-to-apply rules with estimated 30-day matches and the reasoning behind each one.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Precise Triggers and Audiences

Triggers span seven categories, from Whitebait and Blackbait simulation results to identity, endpoint, data loss prevention, directory, training, and risk score events. Filters, occurrence thresholds, and per-person limits shape when a rule fires, and audiences combine presets, departments, groups synced from Microsoft Entra ID, and named individuals.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Stacked Actions With Approval Gates

One rule can assign nudges, modules, videos, policies, or posters, and notify role groups or the triggering employee's manager by email, Microsoft Teams, or both. Higher-stakes actions, such as step-up MFA on next sign-in or a finance approval hold with callback verification, wait for analyst approval every time. Rules can chain, escalating when another rule's action goes unacknowledged.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Zero-Touch Recurring Work

Scheduled rules run weekly, monthly, quarterly, or annually: executive risk reports, policy re-attestation reminders, refresher training reassignments, risk score recalculation, and simulation campaigns, including Blackbait's AI-generated adaptive-difficulty campaigns.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Every Decision Labeled and Logged

Every rule shows whether it is Admin-defined, an AI Recommendation, Agentic AI · Supervised, or Agentic AI · Unsupervised. Every agentic action is logged for audit, and the rule builder shows a plain-language summary, a technical definition, and a warning when a similar rule already exists.

One Step
Ahead of Deceit

Zero-Touch Defense Against Human Risk

Agentic Automation Rules

One engine, three sources of rules, with agentic AI covering whatever the other two miss.

Agentic AI - Agentic Automation Rules

AGENTIC AI

Odin

Agentic AI that responds to human risk the moment it appears. Odin runs the rules you trust, recommends new ones before an incident happens, and steps in on its own when an event falls outside every rule.

‍

  • Writes a contextual rule and runs the intervention the moment an event no rule covers arrives.
  • Three levels of autonomy: off, supervised with approval by email, or unsupervised after a 30-day trial period.
  • Proposes ready-to-apply rules with estimated 30-day matches and the reasoning behind each one.
  • Stacks actions with approval gates, so higher-stakes steps always wait for an analyst.
  • Labels every rule by origin and logs every agentic action for audit.
Explore Odin

Less Administration, Faster Response to Human Risk

Agentic AI takes on the routine work of responding to human risk, while your team keeps the decisions that matter.

Less Administrative Work

Less Administrative Work

Odin assigns training, sends reminders, notifies managers, runs scheduled reports and campaigns, and covers new gaps on its own, so your team stops building and chasing responses by hand.

Faster Intervention

Faster Intervention

Responses go out when the event happens. In Unsupervised mode, uncovered events are handled without waiting for anyone.

Coverage That Grows

Coverage That Grows

Every agentic decision and every accepted recommendation adds a rule, so coverage expands as new risks appear.

Autonomy You Can Audit

Autonomy You Can Audit

Higher-stakes actions wait for analyst approval, every agentic action is logged, and every rule shows whether a person or Odin created it.